

|
시장보고서
상품코드
2124546
보안 평가 : 시장 점유율 분석, 업계 동향과 통계, 성장 예측(2026-2031년)Security Assessment - Market Share Analysis, Industry Trends & Statistics, Growth Forecasts (2026 - 2031) |
||||||
 Mordor Intelligence
에 의하면, 보안 평가 시장 규모는 2025년 48억 7,000만 달러에서 2026년에는 51억 5,000만 달러에 이르고, 2026-2031년 CAGR 5.78%로 성장을 지속하여 2031년에는 68억 3,000만 달러에 달할 것으로 예측됩니다.
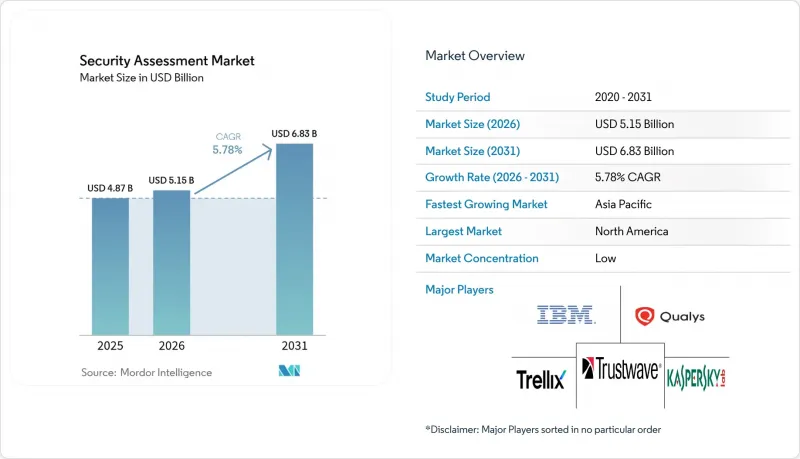
본 보고서는 서비스 유형(취약점 평가, 침투 테스트 등), 도입 모델(On-Premise, 클라우드), 조직 규모(대기업, 중소기업), 최종 사용자 업종(IT 및 통신, 은행, 금융서비스 및 보험(BFSI), 소매 및 전자상거래, 헬스케어 및 생명과학 등) 및 지역별로 분류되어 있습니다. 시장 예측은 금액(달러) 기준으로 제시되어 있습니다.
세계 보안 평가 시장 동향 및 인사이트
피싱/악성코드 공격 건수 및 고도화 추세
의료 기관을 대상으로 한 랜섬웨어 공격은 18개월 동안 137% 급증하여, 기업들은 연례 체크리스트에 그치지 않는 평가 기법을 재고해야 할 상황에 직면해 있습니다. 공격자들은 패치 출시 후 며칠 이내에 전술을 전환하기 때문에 기업들은 정적 스캔 대신 공격자의 행동을 모방한 지속적인 침해 시뮬레이션을 도입하고 있습니다. 아시아태평양은 전 세계적으로 가장 긴 ‘체류 시간’ 중앙값을 기록하고 있어, 전문 평가 서비스가 메워야 할 대응의 공백이 드러나고 있습니다. AI를 활용한 위협 에뮬레이션 및 레드팀 훈련을 제공하는 업체들은 고객들이 정형화된 취약점 스캔보다 현실적인 검증을 요구함에 따라 수주량이 증가하고 있습니다.
규제 준수 의무가 중견 기업으로 확대
2025년 1월부터 시행되고 있는 ‘디지털 운영 복원력 법(Digital Operational Resilience Act)’은 EU 내 22,000개 이상의 금융 기업에 정기적인 복원력 테스트 실시를 의무화하고 있으며, 그 대상이 대형 은행에서 중견 기업으로 확대되고 있습니다. 미국에서는 규제 당국이 제3자 리스크 프로그램을 포함하는 기본적인 복원력 요건을 제시함에 따라, 지역 은행들 사이에서 평가에 대한 새로운 수요가 발생하고 있습니다. 제안된 HIPAA(의료보험 이동성 및 책임에 관한 법률) 보안 개정안에서는 다단계 인증과 연례 감사가 추가로 의무화되어, 첫해의 규정 준수 비용이 90억 달러에 달할 것으로 예측됩니다. 이러한 규제 요건의 확대로 인해 규정 준수 대응이 ‘일시적인 것’에서 ‘지속적인 것’으로 변화하면서 서비스 수요가 안정화되고 있습니다.
중소기업 부문의 예산 제약
중소기업은 매출의 약 4%를 보안에 할당하고 있음에도 불구하고, 불균형적으로 높은 정보 유출률에 직면해 있으며, 아시아태평양 중소기업의 56%가 사고를 보고하고, 75%가 고객 데이터 유출을 겪고 있습니다. 종합적인 테스트는 가용 예산을 초과하는 경우가 많아, 많은 기업이 기본적인 스캐너에 의존할 수밖에 없어 위협 대응 범위에 공백이 발생하고 있습니다. 따라서 비용 효율성에 대한 우려가 단기적인 확장을 제한하는 한편, 도입 비용을 절감하는 자동화된 구독형 플랫폼의 혁신도 촉진하고 있습니다.
부문 분석
취약점 평가는 2025년 매출의 33.02%를 차지하며, 규정 준수 프로그램에서 그 기초적인 역할을 부각시키고 있습니다. 한편, PTaaS는 연평균 성장률(CAGR) 7.18%로 가장 빠르게 성장할 것으로 예상되며, 이는 DevOps에 부합하는 지속적인 검증으로 시장 전환을 반영합니다. 많은 기업이 연 1회 침투 테스트에서 월간 또는 스프린트 단위의 테스트로 전환하고 있습니다. DORA 및 HIPAA 개정으로 인해 위험 및 규정 준수 감사의 도입이 꾸준히 진행되고 있습니다.
멀티 클라우드 환경의 보급에 따라 클라우드 구성 평가에 대한 수요가 증가하고 있습니다. CI/CD 파이프라인에 API를 통합하는 벤더들은 장기적인 컨설팅 주기를 실시간 대시보드로 대체함으로써 지속적인 경쟁 우위를 확보하고 있습니다. AI를 활용한 익스플로잇 생성이 주류화됨에 따라, 구매자의 기대는 작업 시간보다 속도를 중시하는 방향으로 더욱 이동하고 있습니다. 자동화된 감지와 분석가의 검증을 결합한 하이브리드 모델을 제공하는 공급업체는 효율성과 정확성의 균형을 맞추며, BFSI 및 의료와 같은 리스크 회피 성향이 강한 산업에 어필하고 있습니다.
특정 금융 및 정부 기관 고객에게 필수적인 On-Premise 테스트 환경은 2025년 매출의 51.65%를 차지했습니다. 그럼에도 불구하고, 클라우드를 통해 제공되는 평가 플랫폼은 2031년까지 연평균 성장률(CAGR) 7.97%를 나타낼 것으로 전망됩니다. 탄력적인 확장성, 원격 협업, 클라우드 네이티브 워크로드와의 통합이 이러한 확산을 뒷받침하고 있습니다. FedRAMP 20x 로드맵은 공공 부문에서 지속적인 클라우드 모니터링에 대한 수요를 보여주고 있으며, 민간 기업들도 이를 따르고 있습니다. 멀티테넌트형 SaaS 평가는 고객의 인프라 오버헤드를 줄이고 업데이트를 가속화합니다.
멀티클라우드 가시성과 API 개방성을 통해 차별화를 꾀하는 공급업체들은 장기 계약을 확보하고 있습니다. 한편, 하이브리드 근무와 엣지 배포가 확대됨에 따라 순수한 On-Premise형 도구는 구식화될 위험에 직면해 있습니다. 데이터 주권에 관한 규제가 지속되는 지역에서는 벤더들이 규제 대상 고객을 유지하기 위해 하드 에어 갭이 적용된 어플라이언스 대신 주권형 SaaS 리전을 점점 더 많이 구축하고 있습니다.
지역별 분석
북미는 풍부한 예산과 광범위한 규제로 인해 2025년 매출의 40.88%를 차지했습니다. FedRAMP 20x 및 연방 정부의 복원력 기준안은 연방 정부와 은행 부문의 지속적인 모니터링 도입을 촉진하고 있습니다. 캐나다는 USMCA(미국·멕시코·캐나다 협정) 파트너 국가들과 정보 유출 통지 규정을 조율하고 있는 반면, 멕시코의 2024년 데이터 보호법은 공급망 전반에 걸친 표준화된 평가에 대한 수요를 높이고 있습니다.
아시아태평양은 2031년까지 연평균 성장률(CAGR)이 8.27%에 달하며 성장의 원동력이 되고 있습니다. 클라우드의 급속한 보급, 전자상거래의 확대, 지정학적 긴장의 고조가 지출을 끌어올리고 있습니다. 호주와 마이크로소프트 간의 5년간 사이버 보안 협정 및 일본의 국방 중심 사이버 인프라 확충은 자본 투자의 대표적인 사례입니다. 이 지역에서 210만 명의 인력 부족과 공격 체류 시간의 장기화로 인해, 인력 부족을 보완하는 관리형 서비스 및 자동화 서비스에 대한 수요가 증가하고 있습니다. 특히 중소기업은 막대한 설비 투자가 필요 없이 보안 취약점을 해소할 수 있는 구독형 테스트 플랫폼을 선호하고 있습니다.
유럽에서는 근본적인 법규제로 인해 여전히 시장 규모가 큰 상태를 유지하고 있습니다. ‘DORA’는 수천 개의 금융 기관을 대상으로 하며, ‘NIS2’는 유틸리티 및 디지털 제공업체 전반에 걸쳐 의무화되는 보안 대책의 범위를 확대되고 있습니다. 이 지역의 엄격한 데이터 주권 정책으로 인해, 평가 과정에서 현지화된 클라우드 노드 및 암호화된 데이터 스토리지에 대한 수요가 증가하고 있습니다. 영국의 비즈니스 연속성 관련 규정은 EU 법규와 일치하여, 다국적 은행의 경우 유럽 전역에 걸친 규정 준수 로드맵이 간소화되었습니다.
라틴아메리카, 중동 및 아프리카에서는 사이버 사고가 격화되고 각국 정부가 국가 전략을 수립함에 따라, 도입은 초기 단계이지만 빠르게 확대되고 있습니다. 걸프협력회의(GCC) 회원국들은 주권 클라우드 구역에 대한 투자를 추진하고 있으며, 이는 지역 내 평가 수요를 견인하고 있습니다. 남미의 전력 사업자들은 주목을 받은 랜섬웨어 사건을 계기로 중요 인프라 감사를 우선시하고 있습니다. 예산 제약으로 당분간 수익은 제한적이지만, 벤더와 지역 시스템 통합사업자간의 제휴가 중기적인 확장을 위한 기반을 마련하고 있습니다.
기타 혜택:
- 엑셀 형식 시장 예측(ME) 시트
- 3개월간의 애널리스트 지원
자주 묻는 질문
목차
제1장 서론
제2장 조사 방법
제3장 주요 요약
제4장 시장 구도
제5장 시장 규모와 성장 예측
제6장 경쟁 구도
제7장 시장 기회와 향후 전망
LSH 26.09.14According to Mordor Intelligence, the security assessment market size is expected to grow from USD 4.87 billion in 2025 to USD 5.15 billion in 2026 and is forecast to reach USD 6.83 billion by 2031 at 5.78% CAGR over 2026-2031.
This report is Segmented by Service Type (Vulnerability Assessment, Penetration Testing, and More), Deployment Model (On-Premise, Cloud), Organization Size (Large Enterprises, Small and Medium-Sized Enterprises), End-User Vertical (IT and Telecom, BFSI, Retail and ECommerce, Healthcare and Lifesciences, and More), and Geography. The Market Forecasts are Provided in Terms of Value (USD).
Global Security Assessment Market Trends and Insights
Growing Volume and Sophistication of Phishing/Malware Attacks
Ransomware strikes on healthcare providers jumped 137% within 18 months, compelling firms to rethink assessment methods beyond annual checklists. Attackers now pivot tactics within days of patch releases, so enterprises are deploying continuous breach simulation that mirrors adversary behavior instead of static scans. Asia-Pacific records the highest median dwell times globally, exposing response gaps that specialized assessment services must close. Providers delivering AI-backed threat emulation and red-team exercises see rising engagement as clients demand realistic validation over routine vulnerability sweeps.
Regulatory Compliance Mandates Expanding to Mid-Market
The Digital Operational Resilience Act, live since January 2025, obliges more than 22,000 EU financial firms to run regular resilience testing, extending obligations from major banks to mid-tier entities. In the United States, regulators signal baseline resilience requirements that incorporate third-party risk programs, pushing fresh demand for assessment among regional banks. Proposed HIPAA security updates further require multi-factor authentication and yearly audits, projecting USD 9 billion first-year compliance costs. These broadening mandates stabilize service demand by transforming compliance from episodic to ongoing.
Budget Constraints in SMB Segment
Small firms devote near 4% of revenue to security yet face disproportionate breach rates, with 56% of Asia-Pacific SMEs reporting incidents and 75% suffering customer data loss. Full-spectrum testing often exceeds available budgets, pushing many toward basic scanners and leaving gaps in threat coverage. Affordability concerns therefore cap near-term expansion, but they also spur innovation in automated, subscription-priced platforms that lower delivery costs.
Other drivers and restraints analyzed in the detailed report include:
- Surging Cloud Migration Creating Demand for Continuous Validation
- AI-Enabled Automated Testing Platforms Lowering Cost and Cycle Time
- Shortage of Skilled Red-Team/Pentest Talent
For complete list of drivers and restraints, kindly check the Table Of Contents.
Segment Analysis
Vulnerability assessment held 33.02% of 2025 revenue, underscoring its foundational role in compliance programs. PTaaS, however, will scale fastest at 7.18% CAGR, mirroring a market pivot to ongoing validation aligned with DevOps. Many enterprises transition from yearly pentests to monthly or sprint-driven exercises. Risk and compliance audits sustain steady uptake thanks to DORA and HIPAA revisions.
Demand for cloud configuration assessment is rising as multi-cloud estates proliferate. Vendors embedding APIs into CI/CD pipelines create durable advantage, replacing lengthy consulting cycles with real-time dashboards. Mainstream adoption of AI-assisted exploit generation further shifts buyer expectations toward speed over labor hours. Providers offering hybrid models-automated discovery plus analyst validation-balance efficiency and accuracy, appealing to risk-averse sectors like BFSI and healthcare.
On-premise testing environments, mandatory for certain financial and government clients, delivered 51.65% revenue in 2025. Nonetheless, cloud-delivered assessment platforms will post an 7.97% CAGR to 2031. Elastic scale, remote collaboration, and integration with cloud-native workloads drive uptake. The FedRAMP 20x roadmap shows public-sector appetite for continuous cloud monitoring, and private enterprises follow suit. Multi-tenant SaaS assessment reduces infrastructure overhead for clients and accelerates updates.
Providers differentiating through multi-cloud visibility and API openness secure longer-term contracts. Conversely, purely on-premise tools risk obsolescence as hybrid workforces and edge deployments expand. Where data-sovereignty regulations persist, vendors increasingly position sovereign SaaS regions rather than hard-air-gapped appliances to retain regulated customers.
Complete Report Scope:
- By Service Type
- Vulnerability Assessment
- Penetration Testing
- Risk and Compliance Audit
- Red-/Purple-Team Simulation
- Cloud Configuration Assessment
- By Deployment Model
- On-Premise
- Cloud
- By Organization Size
- Large Enterprises
- Small and Medium-Sized Enterprises (SMEs)
- By End-user Industry
- BFSI
- IT and Telecom
- Healthcare and Life Sciences
- Retail and eCommerce
- Energy and Utilities
- Government and Defense
- Others (Education, Media, etc.)
- By Geography
- North America
- United States
- Canada
- Mexico
- South America
- Brazil
- Argentina
- Rest of South America
- Europe
- Germany
- United Kingdom
- France
- Italy
- Spain
- Netherlands
- Russia
- Rest of Europe
- Asia-Pacific
- China
- Japan
- India
- South Korea
- South East Asia
- Australia and New Zealand
- Rest of Asia-Pacific
- Middle East and Africa
- Middle East
- Saudi Arabia
- United Arab Emirates
- Turkey
- Rest of Middle East
- Africa
- South Africa
- Nigeria
- Egypt
- Rest of Africa
- Middle East
- North America
Geography Analysis
North America produced 40.88% of 2025 revenue owing to deep budgets and far-reaching regulations. FedRAMP 20x and potential federal resilience baselines spur federal and banking sectors to adopt continuous monitoring. Canada aligns breach-notification rules with its USMCA partners, while Mexico's 2024 data-protection statute elevates demand for standardized assessment across supply chains.
Asia-Pacific is the growth engine with an 8.27% CAGR through 2031. Rapid cloud adoption, e-commerce expansion, and heightened geopolitical tensions lift spending. Australia's five-year cybersecurity accord with Microsoft and Japan's defense-oriented cyber build-out illustrate capital infusion. The region's 2.1 million talent gap and prolonged dwell times create appetite for managed and automated services that offset staffing deficits. SMEs particularly favor subscription-delivered testing platforms to close exposure gaps without heavy capex.
Europe remains sizable through sweeping legislation. DORA reaches thousands of financial entities, while NIS2 widens compulsory security controls across utilities and digital providers. The region's strict data-sovereignty stance directs demand toward localized cloud nodes and encrypted data storage within assessments. United Kingdom operational-resilience rules converge with EU statutes, simplifying pan-European compliance roadmaps for multinational banks.
Latin America, Middle East, and Africa show nascent yet accelerating uptake as cyber incidents escalate and governments draft national strategies. Gulf Cooperation Council states invest in sovereign cloud zones, driving local assessment demand. South American power utilities prioritize critical-infrastructure audits following headline ransomware incidents. Budget limitations still temper immediate revenue, but vendor partnerships with regional integrators lay groundwork for mid-term expansion.
- IBM Corporation
- Accenture PLC
- Cisco Systems Inc.
- Rapid7 Inc.
- Qualys Inc.
- Check Point Software Technologies Ltd.
- Trustwave (Singtel)
- Optiv Security Inc.
- Mandiant (Google Cloud)
- Secureworks Inc.
- Synopsys Inc.
- CrowdStrike Holdings Inc.
- Fortinet Inc.
- Palo Alto Networks Inc.
- Tenable Holdings Inc.
- Veracode
- Snyk Ltd.
- Absolute Software Corp.
- Holm Security
- Kaspersky Lab
- FireEye/Trellix
Additional Benefits:
- The market estimate (ME) sheet in Excel format
- 3 months of analyst support
TABLE OF CONTENTS
1 INTRODUCTION
- 1.1 Study Assumptions and Market Definition
- 1.2 Scope of the Study
2 RESEARCH METHODOLOGY
3 EXECUTIVE SUMMARY
4 MARKET LANDSCAPE
- 4.1 Market Overview
- 4.2 Market Drivers
- 4.2.1 Growing volume and sophistication of phishing/malware attacks
- 4.2.2 Regulatory compliance mandates expanding to mid-market (e.g., DORA, OCC resilience rules)
- 4.2.3 Surging cloud migration driving continuous security validation demand
- 4.2.4 AI-enabled automated testing platforms lowering cost and cycle time
- 4.2.5 Pen-Testing-as-a-Service (PTaaS) adoption among SaaS vendors
- 4.2.6 Convergence of DevSecOps and shift-left security testing
- 4.3 Market Restraints
- 4.3.1 Budget constraints in SMB segment
- 4.3.2 Shortage of skilled red-team/pentest talent
- 4.3.3 Tool sprawl leading to assessment fatigue" and alert overload"
- 4.3.4 Accuracy concerns around Gen-AI-driven assessment engines
- 4.4 Industry Ecosystem Analysis
- 4.5 Technological Outlook
- 4.6 Porter's Five Forces Analysis
- 4.6.1 Threat of New Entrants
- 4.6.2 Bargaining Power of Buyers
- 4.6.3 Bargaining Power of Suppliers
- 4.6.4 Threat of Substitutes
- 4.6.5 Intensity of Competitive Rivalry
5 MARKET SIZE AND GROWTH FORECASTS (VALUES)
- 5.1 By Service Type
- 5.1.1 Vulnerability Assessment
- 5.1.2 Penetration Testing
- 5.1.3 Risk and Compliance Audit
- 5.1.4 Red-/Purple-Team Simulation
- 5.1.5 Cloud Configuration Assessment
- 5.2 By Deployment Model
- 5.2.1 On-Premise
- 5.2.2 Cloud
- 5.3 By Organization Size
- 5.3.1 Large Enterprises
- 5.3.2 Small and Medium-Sized Enterprises (SMEs)
- 5.4 By End-user Industry
- 5.4.1 BFSI
- 5.4.2 IT and Telecom
- 5.4.3 Healthcare and Life Sciences
- 5.4.4 Retail and eCommerce
- 5.4.5 Energy and Utilities
- 5.4.6 Government and Defense
- 5.4.7 Others (Education, Media, etc.)
- 5.5 By Geography
- 5.5.1 North America
- 5.5.1.1 United States
- 5.5.1.2 Canada
- 5.5.1.3 Mexico
- 5.5.2 South America
- 5.5.2.1 Brazil
- 5.5.2.2 Argentina
- 5.5.2.3 Rest of South America
- 5.5.3 Europe
- 5.5.3.1 Germany
- 5.5.3.2 United Kingdom
- 5.5.3.3 France
- 5.5.3.4 Italy
- 5.5.3.5 Spain
- 5.5.3.6 Netherlands
- 5.5.3.7 Russia
- 5.5.3.8 Rest of Europe
- 5.5.4 Asia-Pacific
- 5.5.4.1 China
- 5.5.4.2 Japan
- 5.5.4.3 India
- 5.5.4.4 South Korea
- 5.5.4.5 South East Asia
- 5.5.4.6 Australia and New Zealand
- 5.5.4.7 Rest of Asia-Pacific
- 5.5.5 Middle East and Africa
- 5.5.5.1 Middle East
- 5.5.5.1.1 Saudi Arabia
- 5.5.5.1.2 United Arab Emirates
- 5.5.5.1.3 Turkey
- 5.5.5.1.4 Rest of Middle East
- 5.5.5.2 Africa
- 5.5.5.2.1 South Africa
- 5.5.5.2.2 Nigeria
- 5.5.5.2.3 Egypt
- 5.5.5.2.4 Rest of Africa
- 5.5.5.1 Middle East
- 5.5.1 North America
6 COMPETITIVE LANDSCAPE
- 6.1 Market Concentration
- 6.2 Strategic Moves
- 6.3 Market Share Analysis
- 6.4 Company Profiles (includes Global level Overview, Market level overview, Core Segments, Financials as available, Strategic Information, Market Rank/Share, Products and Services, Recent Developments)
- 6.4.1 IBM Corporation
- 6.4.2 Accenture PLC
- 6.4.3 Cisco Systems Inc.
- 6.4.4 Rapid7 Inc.
- 6.4.5 Qualys Inc.
- 6.4.6 Check Point Software Technologies Ltd.
- 6.4.7 Trustwave (Singtel)
- 6.4.8 Optiv Security Inc.
- 6.4.9 Mandiant (Google Cloud)
- 6.4.10 Secureworks Inc.
- 6.4.11 Synopsys Inc.
- 6.4.12 CrowdStrike Holdings Inc.
- 6.4.13 Fortinet Inc.
- 6.4.14 Palo Alto Networks Inc.
- 6.4.15 Tenable Holdings Inc.
- 6.4.16 Veracode
- 6.4.17 Snyk Ltd.
- 6.4.18 Absolute Software Corp.
- 6.4.19 Holm Security
- 6.4.20 Kaspersky Lab
- 6.4.21 FireEye/Trellix
7 MARKET OPPORTUNITIES AND FUTURE OUTLOOK
- 7.1 White-space and Unmet-need Assessment


