|
시장보고서
상품코드
2125727
유럽의 SOCaaS(Security Operation Center As A Service) 시장 : 시장 점유율 분석, 업계 동향 및 통계, 성장 예측(2026-2031년)Europe SOC As A Service (SOCaaS) - Market Share Analysis, Industry Trends & Statistics, Growth Forecasts (2026 - 2031) |
||||||
 Mordor Intelligence
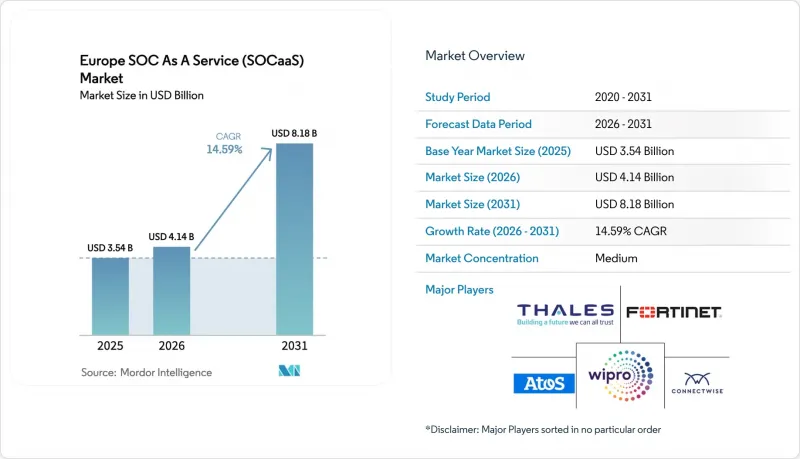
에 의하면, 유럽의 SOCaaS(Security Operation Center As A Service) 시장 규모는 2025년에 35억 4,000만 달러로 평가되었고, 2026년에 41억 4,000만 달러로 추정되고, 2031년까지 81억 8,000만 달러에 이를 것으로 예측되며, 2026-2031년 CAGR 14.59%로 성장할 전망입니다.
본 보고서는 조직 규모별(중소기업 및 대기업), 최종 사용자별(IT 및 통신, 은행, 금융서비스 및 보험(BFSI), 기타), 서비스 유형별(관리형 감지 및 대응, 기타), 배포 방식별(클라우드, 온프레미스, 하이브리드), 보안 유형별(네트워크 보안, 엔드포인트 보안, 기타), 지역별로 분류되어 있습니다. 시장 전망은 금액(달러) 기준으로 제시되어 있습니다.
유럽의 SOCaaS(Security Operation Center As A Service) 시장 동향 및 인사이트
EU의 NIS2 규정 준수 요건
NIS2에 따라 규제 대상 조직의 수는 약 2,000개에서 16만 개 이상으로 확대되었으며, 중규모 유틸리티체, 병원, 운송 사업자조차도 지속적인 모니터링 체제를 유지해야 할 의무가 부과되었고, 위반 시 최대 1,000만 유로(1,070만 달러)의 벌금이 부과되게 되었습니다. 이러한 조직 중 24시간 체제로 사내 SOC를 운영할 수 있는 곳은 거의 없기 때문에 감사 대응이 완료된 대시보드와 자동화된 사고 보고 기능을 제공하는 공급업체에게는 지속적인 수요 기반이 확보되어 있습니다. 독일과 프랑스의 규제 당국은 국내 데이터 레지던시 규정을 통해 이 지침을 보완하고 있으며, 사실상 각국 내에 데이터센터를 운영하는 벤더와의 계약을 유도하고 있습니다. 미국의 3일 보고 유예 기간과 비교할 때, 유럽의 24시간 보고 기한은 긴급성을 높여, AI를 활용한 감지 기능에 대한 프리미엄 가격 책정을 정당화하는 요인이 되고 있습니다.
중소기업의 급속한 클라우드 전환
유로스타트(Eurostat) 기록에 따르면, 직원 수십 명에서 249명 규모의 EU 기업 중 45%가 2024년에 클라우드 서비스를 이용하고 있으며, 이는 3년 전 38%에서 증가한 수치입니다. 이러한 확대로 인해 기존의 경계가 모호해졌으며, 레거시 방화벽으로는 감지할 수 없는 ID 및 API 계층이 노출되고 있습니다. 예산 제약이 있는 중소기업은 전담 보안 전문가를 배치하는 경우가 거의 없지만, 대기업과 마찬가지로 랜섬웨어의 급증에 직면해 있습니다. 따라서 Microsoft 365나 Google Workspace 내의 워크로드를 자동으로 감지하는 SOCaaS 플랫폼을 도입함으로써, 예측 가능한 월정액 요금으로 높은 수준의 보호를 확보할 수 있습니다. 도구 및 인건비를 포함한 평균 총 소유 비용은 사내 구축 비용의 약 6분의 1 수준이어서 명확한 경제적 이점이 있습니다.
사이버 보안 인력 부족
2025년, 유럽에서는 약 35만 명의 사이버 보안 전문가가 부족한 것으로 평가되었으며, 주요 경제국에서 Tier 2 분석가를 채용하는 데 걸리는 기간의 중앙값은 4개월을 초과했습니다. 임금 상승으로 인해 서비스 제공업체의 비용이 증가하고 있으며, 일부 벤더는 인력 확보 체제가 갖춰질 때까지 신규 고객 수용을 제한하고 있습니다. 해결책으로는 루마니아나 불가리아로의 니어쇼어링, 고도화된 자동화, 2027년까지 연간 200명의 졸업생을 목표로 하는 Orange Cyberdefense의 듀얼 트랙 석사 과정과 같은 대학과의 제휴 등이 있습니다. 이러한 대책에도 불구하고, 인력 수 제한으로 인해 채용 속도가 느려져 대규모 사고 발생 시 서비스 품질이 저하될 우려가 있습니다.
부문 분석
현재 중소기업의 총 지출에서 차지하는 비중은 그리 크지 않지만, 2026-2031년 연평균 성장률(CAGR) 15.68%를 나타낼 것으로 예측되며, 수요 증가분에서는 대기업을 능가할 것으로 전망됩니다. 많은 중소기업이 2024년이 되어서야 비로소 NIS2 적용 대상이 되었으며, 합리적인 가격의 연중무휴 24시간 모니터링 서비스를 요구하는 움직임이 활발해졌습니다. 2025년에 출시된 Arctic Wolf의월5,000달러 정액제 패키지는 이벤트 발생량에 따른 예측 불가능한 가격 변동을 해소하여, 사용자 수가 250명 이하인 기업들로부터 호평을 얻고 있습니다. 대조적으로, 이미 사내 SOC를 운영하고 있는 대기업은 주로 버스트 용량이나 전문적인 기능을 외부에 위탁하고 있기 때문에 그 성장률은 둔화되고 있습니다. 대기업의 인프라는 여러 데이터센터, 클라우드, 운영 기술(OT) 네트워크에 걸쳐 있기 때문에 2025년 유럽 SOCaaS 시장 점유율의 58.38%를 여전히 차지하고 있습니다.
각 제공업체는 저마다 다른 시장 진출 전략을 펼치고 있습니다. 중소기업을 대상으로 벤더들은 ‘가치 실현까지 걸리는 시간’, 안내식 설정 마법사, 전문 서비스 없이도 Microsoft 365 및 Salesforce와 연동할 수 있는 사전 설정된 플레이북을 강조하고 있습니다. 반면, 세계 복합 기업을 대상으로는 맞춤형 서비스 수준 계약(SLA), 위협 인텔리전스 구독, 경영진을 위한 시뮬레이션 훈련을 중심으로 계약 내용이 구성됩니다. 그 결과, 중소기업이 차지하는 유럽 SOCaaS 시장 규모는 2031년까지 약 3배로 확대될 것으로 예상되는 반면, 대기업의 지출은 약 2배로 증가할 것으로 전망됩니다.
은행 및 금융 서비스 및 보험 산업은 디지털 운영 복원력 법(Digital Operational Resilience Act)의 영향으로 2025년에는 매출의 24.53%를 차지하며 계속해서 최대 지출 부문으로 남아 있습니다. 그러나 가장 빠르게 성장하고 있는 분야는 의료 분야로, 2031년까지 연평균 성장률(CAGR) 15.01%로 확대되고 있습니다. 병원을 표적으로 한 랜섬웨어 공격은 2023-2025년 210% 증가하여, 그동안 사이버 보안에 대한 투자가 부족했던 의료 네트워크가 다년간의 SOCaaS 계약을 체결할 수밖에 없게 만들고 있습니다. 보험 계약 갱신 시에는 24시간 365일 모니터링 체제가 문서로 증명되어야 하는 것이 요구되고 있으며, 이로 인해 잠재 고객의 계약 성사율이 향상되고 있습니다.
한편, 제조업 기업들은 로깅 기능이 없는 레거시 프로그래머블 로직 컨트롤러(PLC)의 통합에 어려움을 겪고 있으며,도입 속도는 둔화되고 있지만, 그와 동시에 Fortinet이 2025년에 출시한 ‘FortiSOC’와 같은 운영 기술(OT)에 대응하는 솔루션에 대한 틈새 수요가 발생하고 있습니다. 국가 예산에서 전용 자금이 배정됨에 따라 정부 기관의 구매자층은 확대되고 있지만, 지자체 간 조달 체계의 불균일성이 즉각적인 도입을 저해하고 있습니다.
기타 혜택
- 엑셀 형식 시장 예측(ME) 시트
- 3개월간의 애널리스트 지원
자주 묻는 질문
목차
제1장 서론
제2장 조사 방법
제3장 주요 요약
제4장 시장 구도
제5장 시장 규모 및 성장 예측
제6장 경쟁 구도
제7장 시장 기회 및 향후 전망
AJY 26.09.15According to Mordor Intelligence, the Europe SOC as a Service market size is projected to be USD 3.54 billion in 2025, USD 4.14 billion in 2026, and reach USD 8.18 billion by 2031, growing at a CAGR of 14.59% from 2026 to 2031.
This report is Segmented by Organization Size (Small and Medium-Sized Enterprises, and Large Enterprises), End User (IT and Telecom, BFSI, and More), Service Type (Managed Detection and Response, and More), Deployment Mode (Cloud, On-Premise, and Hybrid), Security Type (Network Security, Endpoint Security, and More), and Geography. The Market Forecasts are Provided in Terms of Value (USD).
Europe SOC As A Service (SOCaaS) Market Trends and Insights
EU NIS2 Compliance Mandate
NIS2 widened the pool of regulated entities from roughly 2,000 to more than 160,000, compelling even mid-sized utilities, hospitals, and transport operators to maintain continuous monitoring or face fines up to EUR 10 million (USD 10.7 million). As few of these organizations can staff an in-house SOC around the clock, providers offering audit ready dashboards and automated incident reporting enjoy a sustained demand floor. German and French regulators reinforce the directive with national data-residency rules, effectively steering contracts toward vendors running data centers inside each country. Compared with the United States three-day reporting allowance, Europe's 24-hour window increases urgency and justifies premium pricing for AI enhanced detection.
Rapid Cloud Migration Among SMEs
Eurostat recorded that 45% of EU firms with 10-249 employees used cloud services in 2024, up from 38% three years earlier. This expansion dissolves the traditional perimeter, exposing identity and API layers that legacy firewalls miss. Budget constrained SMEs rarely field a dedicated security professional yet face the same ransomware surge as larger peers. Onboarding to SOCaaS platforms that auto-discover workloads inside Microsoft 365 or Google Workspace therefore offers high protection for a predictable monthly fee. Average total cost of ownership, including tooling and staff, runs roughly one-sixth of an in-house build, creating a clear economic argument.
Cyber Talent Scarcity
Europe lacked roughly 350,000 cybersecurity professionals in 2025, and median hiring time for a tier-two analyst exceeded four months in major economies. Wage inflation raises provider costs, and some vendors cap new customer intake until staffing pipelines catch up. Solutions include near-shoring to Romania and Bulgaria, heavy automation, and university partnerships like Orange Cyberdefense's dual-track master's program targeting 200 graduates per year by 2027. Despite these tactics, limited headcount slows onboarding speed and can constrain service quality during major incident surges.
Other drivers and restraints analyzed in the detailed report include:
- Generative-AI Threat Hunting
- XDR Bundling by Telcos and MSPs
- Data Residency and Sovereignty Rules
For complete list of drivers and restraints, kindly check the Table Of Contents.
Segment Analysis
Small and medium-sized enterprises account for a modest portion of total spending today, yet they are forecast to grow at a 15.68% CAGR between 2026 and 2031, overtaking large enterprises in incremental demand. Many SMEs came under NIS2 jurisdiction only in 2024, triggering a scramble for affordable 24x7 monitoring. Arctic Wolf's fixed-fee bundle at USD 5,000 per month, launched in 2025, removes unpredictable event-volume pricing and resonates with firms managing fewer than 250 users. In contrast, large enterprises that already run internal SOCs primarily outsource burst capacity or specialized functions, which tempers their growth rate. Nonetheless, big firms still represent 58.38% of Europe's SOC As A Service market share in 2025 because their infrastructures span multiple data centers, clouds, and operational technology networks.
Providers deploy separate go-to-market motions. For SMEs, vendors stress time to value, guided setup wizards, and pre-configured playbooks that attach to Microsoft 365 and Salesforce without professional services. For global conglomerates, contracts revolve around bespoke service level agreements, threat intelligence subscriptions, and executive tabletop exercises. As a result, the Europe SOC As A Service market size captured by SMEs is expected to almost triple by 2031, while large enterprise spending roughly doubles.
Banking financial services and insurance entities remain the top spenders, holding 24.53% of revenue in 2025 thanks to the Digital Operational Resilience Act. Yet healthcare is the fastest climber, advancing at 15.01% CAGR through 2031. Ransomware campaigns targeting hospitals rose 210% between 2023 and 2025, forcing clinical networks that historically underinvested in cybersecurity to sign multi-year SOCaaS contracts. Insurance renewals now require documented 24x7 monitoring, driving up funnel conversion.
Meanwhile, manufacturing firms struggle to integrate legacy programmable logic controllers that lack logging, slowing uptake but opening niche demand for OT aware offerings like Fortinet's 2025 FortiSOC launch. Government buyers expand as national budgets allocate ring fenced funds, but procurement fragmentation across municipalities tempers immediate adoption.
Complete Report Scope:
- By Organization Size
- Small and Medium-Sized Enterprises
- Large Enterprises
- By End User
- IT and Telecom
- BFSI
- Retail and Consumer Goods
- Healthcare
- Manufacturing
- Government
- Other End Users
- By Service Type
- Managed Detection and Response
- Security Monitoring
- Vulnerability Assessment
- Incident Response
- Threat Intelligence
- Managed SIEM
- Other Service Types
- By Deployment Mode
- Cloud
- On-Premise
- Hybrid
- By Security Type
- Network Security
- Endpoint Security
- Application Security
- Cloud Security
- Other Security Types
- By Country
- Germany
- United Kingdom
- France
- Italy
- Spain
- Netherlands
- Austria
- Belgium
- Sweden
- Rest of Europe
List of Companies Covered in this Report:
- IBM Corporation
- SecureWorks Inc.
- Fortinet Inc.
- Atos SE
- Thales Group
- Wipro Limited
- Cloudflare Inc.
- ConnectWise LLC
- Sophos Limited
- Ontinue Inc.
- PlusServer GmbH
- Teceze Limited
- Arctic Wolf Networks Inc.
- Rapid7 Inc.
- Orange Cyberdefense SA
- NTT Security Holdings Corporation
- Accenture PLC
- Telefonica Tech S.L.U.
- Deloitte Touche Tohmatsu Limited
- KPMG International Limited
Additional Benefits:
- The market estimate (ME) sheet in Excel format
- 3 months of analyst support
TABLE OF CONTENTS
1 INTRODUCTION
- 1.1 Study Assumptions and Market Definition
- 1.2 Scope of the Study
2 RESEARCH METHODOLOGY
3 EXECUTIVE SUMMARY
4 MARKET LANDSCAPE
- 4.1 Market Overview
- 4.2 Impact of Macroeconomic Factors
- 4.3 Industry Value-Chain Analysis
- 4.4 Regulatory Landscape
- 4.5 Technological Outlook
- 4.6 Porter's Five Forces Analysis
- 4.6.1 Threat of New Entrants
- 4.6.2 Bargaining Power of Buyers
- 4.6.3 Bargaining Power of Suppliers
- 4.6.4 Threat of Substitutes
- 4.6.5 Competitive Rivalry
- 4.7 Market Drivers
- 4.7.1 Rise in Adoption of Pay-per-Use Opex Model
- 4.7.2 Rapid Cloud Migration Among SMEs
- 4.7.3 Mounting Cyber-Insurance Prerequisites for 24x7 Monitoring
- 4.7.4 EU NIS2 Directive Amplifying Compliance Demand
- 4.7.5 Generative AI-Powered Threat Hunting Capabilities
- 4.7.6 Surge in Managed XDR Bundling by Telcos and MSPs
- 4.7.7 Increasing Availability of Sovereign European Clouds
- 4.8 Market Restraints
- 4.8.1 Data Residency and Sovereignty Complexities
- 4.8.2 Scarcity of European SOC-Grade Cyber Talent
- 4.8.3 Hidden Long-Term TCO in Multi-Tenant SIEM
- 4.8.4 Integration Friction with Legacy OT Environments
5 MARKET SIZE AND GROWTH FORECASTS (VALUE)
- 5.1 By Organization Size
- 5.1.1 Small and Medium-Sized Enterprises
- 5.1.2 Large Enterprises
- 5.2 By End User
- 5.2.1 IT and Telecom
- 5.2.2 BFSI
- 5.2.3 Retail and Consumer Goods
- 5.2.4 Healthcare
- 5.2.5 Manufacturing
- 5.2.6 Government
- 5.2.7 Other End Users
- 5.3 By Service Type
- 5.3.1 Managed Detection and Response
- 5.3.2 Security Monitoring
- 5.3.3 Vulnerability Assessment
- 5.3.4 Incident Response
- 5.3.5 Threat Intelligence
- 5.3.6 Managed SIEM
- 5.3.7 Other Service Types
- 5.4 By Deployment Mode
- 5.4.1 Cloud
- 5.4.2 On-Premise
- 5.4.3 Hybrid
- 5.5 By Security Type
- 5.5.1 Network Security
- 5.5.2 Endpoint Security
- 5.5.3 Application Security
- 5.5.4 Cloud Security
- 5.5.5 Other Security Types
- 5.6 By Country
- 5.6.1 Germany
- 5.6.2 United Kingdom
- 5.6.3 France
- 5.6.4 Italy
- 5.6.5 Spain
- 5.6.6 Netherlands
- 5.6.7 Austria
- 5.6.8 Belgium
- 5.6.9 Sweden
- 5.6.10 Rest of Europe
6 COMPETITIVE LANDSCAPE
- 6.1 Market Concentration
- 6.2 Strategic Moves
- 6.3 Market Share Analysis
- 6.4 Company Profiles (includes Global Level Overview, Market Level Overview, Core Segments, Financials as available, Strategic Information, Market Rank/Share, Products and Services, Recent Developments)
- 6.4.1 IBM Corporation
- 6.4.2 SecureWorks Inc.
- 6.4.3 Fortinet Inc.
- 6.4.4 Atos SE
- 6.4.5 Thales Group
- 6.4.6 Wipro Limited
- 6.4.7 Cloudflare Inc.
- 6.4.8 ConnectWise LLC
- 6.4.9 Sophos Limited
- 6.4.10 Ontinue Inc.
- 6.4.11 PlusServer GmbH
- 6.4.12 Teceze Limited
- 6.4.13 Arctic Wolf Networks Inc.
- 6.4.14 Rapid7 Inc.
- 6.4.15 Orange Cyberdefense SA
- 6.4.16 NTT Security Holdings Corporation
- 6.4.17 Accenture PLC
- 6.4.18 Telefonica Tech S.L.U.
- 6.4.19 Deloitte Touche Tohmatsu Limited
- 6.4.20 KPMG International Limited
7 MARKET OPPORTUNITIES AND FUTURE OUTLOOK
- 7.1 White-Space and Unmet-Need Assessment